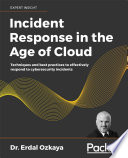
Incident Response in the Age of Cloud: Techniques and best practices to effectively respond to cybersecurity incidents
Erdal OzkayaIncident Response in the Age of Cloud: Techniques and best practices to effectively respond to cybersecurity incidents
or to grade, review, and add to your backlog.
Description
Learn to identify security incidents and build a series of best practices to stop cyber attacks before they create serious consequences Key FeaturesDiscover Incident Response (IR), from its evolution to implementationUnderstand cybersecurity essentials and IR best practices through real-world phishing incident scenariosExplore the current challenges in IR through the perspectives of leading expertsBook Description Cybercriminals are always in search of new methods to infiltrate systems. Quickly responding to an incident will help organizations minimize losses, decrease vulnerabilities, and rebuild services and processes. In the wake of the COVID-19 pandemic, with most organizations gravitating towards remote working and cloud computing, this book uses frameworks such as MITRE ATT&CK® and the SANS IR model to assess security risks. The book begins by introducing you to the cybersecurity landscape and explaining why IR matters. You will understand the evolution of IR, current challenges, key metrics, and the composition of an IR team, along with an array of methods and tools used in an effective IR process. You will then learn how to apply these strategies, with discussions on incident alerting, handling, investigation, recovery, and reporting. Further, you will cover governing IR on multiple platforms and sharing cyber threat intelligence and the procedures involved in IR in the cloud. Finally, the book concludes with an “Ask the Experts” chapter wherein industry experts have provided their perspective on diverse topics in the IR sphere. By the end of this book, you should become proficient at building and applying IR strategies pre-emptively and confidently. What you will learnUnderstand IR and its significanceOrganize an IR teamExplore best practices for managing attack situations with your IR teamForm, organize, and operate a product security team to deal with product vulnerabilities and assess their severityOrganize all the entities involved in product security responseRespond to security vulnerabilities using tools developed by Keepnet Labs and BinalyzeAdapt all the above learnings for the cloudWho this book is for This book is aimed at first-time incident responders, cybersecurity enthusiasts who want to get into IR, and anyone who is responsible for maintaining business security. It will also interest CIOs, CISOs, and members of IR, SOC, and CSIRT teams. However, IR is not just about information technology or security teams, and anyone with a legal, HR, media, or other active business role would benefit from this book. The book assumes you have some admin experience. No prior DFIR experience is required. Some infosec knowledge will be a plus but isn’t mandatory.
Community reviews
No reviews yet. Be the first to review this book.
More like this
- Next Level
Next Level
Michael Cook

The Year in Tech, 2025: The Insights You Need from Harvard Business Review
Harvard Business Review

The Heart and the Chip: Our Bright Future with Robots
Daniela Rus
The Mind's Mirror: Risk and Reward in the Age of AI
Daniela Rus

After Digital: Computation as Done by Brains and Machines
James A. Anderson

Prompt Engineering for LLMs: The Art and Science of Building Large Language Model-Based Applications
John Berryman

Don't Burn Anyone At The Stake Today: (and other lessons from history about living through an information crisis)
Naomi Alderman
Twitch For Dummies
Tee Morris